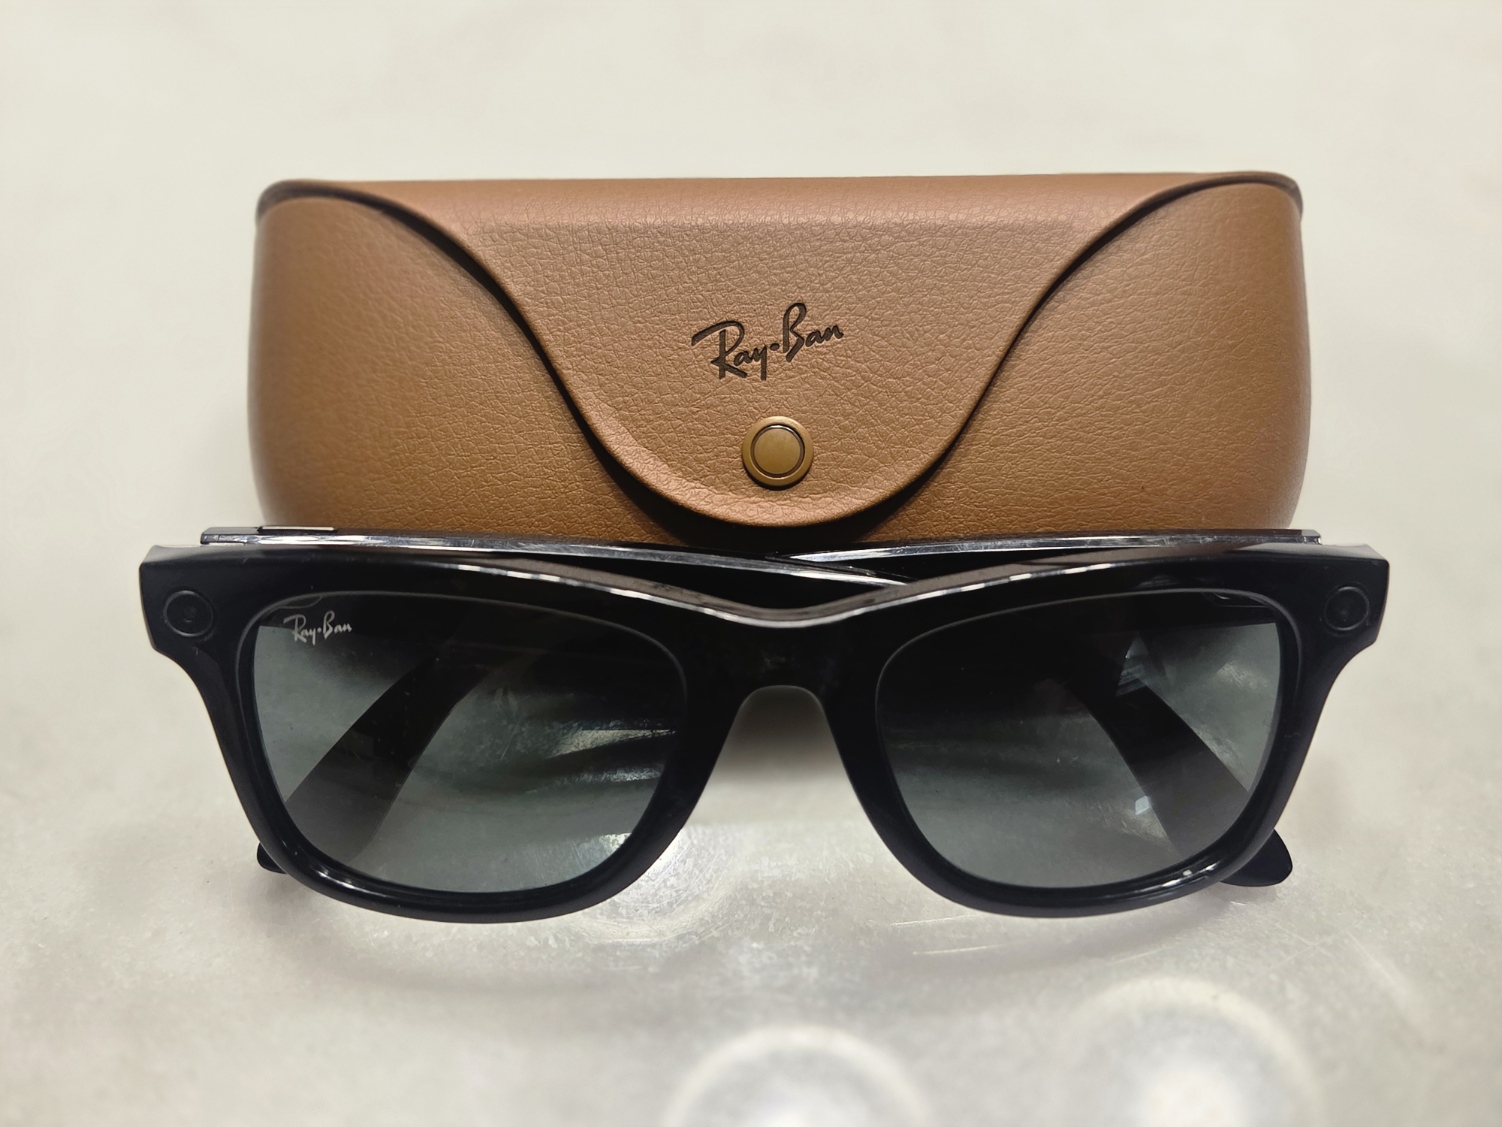
Cybernews published a comparison of SEVEN AI smart-glasses companion apps on October 6, and its headline finding is that the Meta AI app, the one Ray-Ban Meta owners MUST install, asks for MORE Android permissions than any of its Chinese rivals. The numbers HOLD UP: Exodus Privacy, the nonprofit audit platform Cybernews drew on, lists 70 permissions for Meta AI, 18 of them flagged DANGEROUS. What the article does NOT say is which build was scanned. Exodus dates its Meta AI report to September 11, 2026, on version 289.0.0.25.162, and the app has SHIPPED NEWER releases since.

What Cybernews Counted
The Cybernews analysis, by senior journalist Eglė Krištopaitytė, covers Meta, Rokid, RayNeo, INMO, Solos, Even Realities and Halliday. On TOTAL permissions it ranks Meta AI FIRST at 70, followed by Even Realities at 61, Solos AirGo at 55 and Hi Rokid at 53. Halliday asks for ONLY 32, but 12 of those, or 38%, are in Android’s dangerous class. Cybernews is CAREFUL to define that label as anything requiring explicit runtime consent, “but not proof of misuse.”
Trackers tell a DIFFERENT story. Exodus finds just ONE tracker signature in Meta AI, Facebook Flipper, which Cybernews describes as Meta’s own debugging tool rather than a third-party ad or analytics kit. INMO Global and Solos AirGo carry SIX trackers each; Solos alone embeds three separate Meta/Facebook SDKs for analytics, login and sharing, plus Google Firebase Analytics and Crashlytics. Hi Rokid is the only app in the set with ZERO trackers detected.
What the Exodus Report Actually Shows
Metaverse Watcher DIRECTLY checked the Exodus report for Meta AI (package com.facebook.stella). The 18 permissions marked dangerous include background, coarse and fine LOCATION; CAMERA and RECORD_AUDIO; READ_CONTACTS, GET_ACCOUNTS and READ_PHONE_STATE; READ_CALL_LOG; and a full SMS set of READ_SMS, RECEIVE_SMS, RECEIVE_MMS and SEND_SMS. The Hi Rokid report, also dated September 11 on version G1.13.8.0828, flags 13 dangerous permissions, including background location, camera, microphone, contacts and READ/WRITE calendar access, but NO SMS or call-log access.
TWO caveats matter. First, Exodus is a STATIC audit: it reads what an app declares in its manifest and which tracker code signatures appear in it. It does NOT observe what data actually LEAVES the phone, and neither Cybernews nor Exodus ties any single permission to a specific glasses feature. Second, the snapshot is DATED. Metaverse Watcher reported Meta AI 292.1.0 on October 4, when Meta added email and calendar features to the same app. Any build that reaches into mail and calendars could plausibly request MORE access, not less, but NOBODY has published a scan of it yet, so the 70 figure should be read as a September baseline, not the CURRENT count.

The Privacy Scorecard Beyond the Phone
Cybernews also scored each brand from 0 to 2 against NINE criteria it says were drawn from Apple’s reported approach to its own AI glasses, including camera indicators, on-device processing, facial recognition, AI training, human review and data retention, using privacy policies, product pages and independent reviews. Several findings STAND OUT:
- Only Meta and Rokid have a CONFIRMED response when the recording LED is covered. RayNeo and Solos do NOT address it. Meta’s late-August software update STOPS recording when the light is BLOCKED.
- ALL seven brands run their core AI features, such as voice, translation and image analysis, in the CLOUD; NONE processes them LOCALLY on the glasses.
- FIVE of seven do not specify any data-retention limit. Even Realities is the ONLY one that discloses immediate deletion of captured voice by default; Meta caps some data at 30 days to a year.
- Only Meta, Rokid and Even Realities publish a privacy document written SPECIFICALLY for their glasses. RayNeo and Halliday rely ENTIRELY on GENERIC company-wide policies.
NO facial-recognition function was DETECTED in any of the seven devices, Cybernews says, although it cites Wired’s August report that an INACTIVE face-recognition pipeline sits inside Meta’s companion app, which Meta called an “ongoing exploration.”
Why It Lands This Week
The comparison arrives in the SAME news cycle as Australia’s privacy commissioner opening a formal investigation into Shenzhen Qingcheng, the maker of the HeyCyan app behind cheap glasses sold through Kmart, and Norway’s proposal for a temporary ban on AI glasses in parks, schools, gyms and shopping centres. Regulators so far have focused on the people being FILMED. The Cybernews data shifts part of the question to the WEARER, whose phone grants the companion app its reach.
The fair reading is NARROW. Meta’s app asks for the BROADEST Android footprint in this group but carries almost NO third-party tracking; smaller rivals ask for less while embedding MORE outside SDKs. Neither metric PROVES misuse. A fresh Exodus scan of the current Meta AI build, and a per-feature explanation from Meta of why a glasses app needs SMS and call-log access, would SETTLE more than another ranking.
Sources: Cybernews, October 6, 2026; Exodus Privacy, Meta AI report; Exodus Privacy, Hi Rokid report; Cybernews on Norway’s proposal.