By MetaverseWatcher Staff · November 13, 2026
If your Apple Vision Pro hasn’t installed visionOS 27.2.1 yet, now is the time. Apple’s short release note describes the November 9 update as “bug fixes and security updates.” Its security content page lists nine fixes. One patches CVE-2026-111497, a memory-corruption bug in the open-source Brotli compression library. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has listed that CVE in its Known Exploited Vulnerabilities catalog. Four more fixes cover attacks from within Bluetooth range.
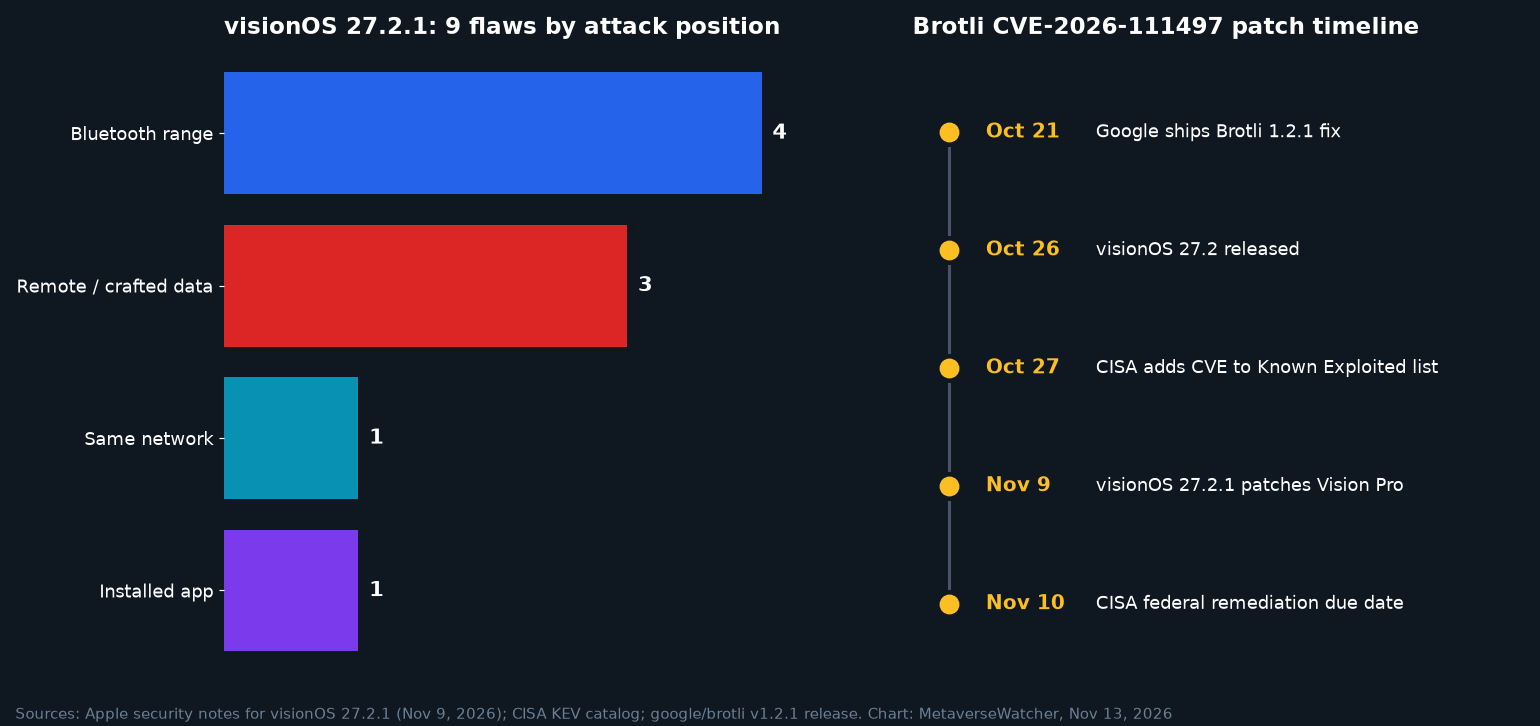
What visionOS 27.2.1 fixes
Apple says every fix applies to “Apple Vision Pro (all models).” We grouped the nine by where an attacker would need to be, based on the impact statements in Apple’s notes:
| Component | CVE | Impact (Apple’s wording, condensed) |
|---|---|---|
| brotli | CVE-2026-111497 | Maliciously crafted input may lead to memory corruption (out-of-bounds write) |
| CoreUtils | CVE-2026-113965 | A malicious Bluetooth device may pair without user interaction |
| CoreUtils | CVE-2026-113964 | Attacker in Bluetooth range may bypass pairing-code rate limits and pair without user interaction |
| Bluetooth | CVE-2026-113970 | Attacker in Bluetooth range may corrupt process memory (use-after-free) |
| AirPlay | CVE-2026-113968 | Attacker in Bluetooth range may bypass the pairing-code rate limit |
| rapportd | CVE-2026-113969 | Attacker on the same network may bypass the AirPlay pairing-code rate limit |
| Messages | CVE-2026-113961 | Remote attacker may join an iMessage group chat and receive its messages |
| Messages | CVE-2026-113960 | A user added to a group may read messages sent before they joined |
| App Intents | CVE-2026-113963 | An app may access sensitive user data |
The Bluetooth group matters more on a headset than on most devices. Vision Pro owners routinely pair keyboards, trackpads, game controllers and AirPods, and the headset is often used in shared spaces like offices, planes and hotels. That is exactly where an attacker within radio range is plausible.
Why the Brotli fix stands out
Brotli is Google’s compression format, widely used for web content and built into many operating systems, browsers and runtimes. Google’s Brotli 1.2.1 release on October 21 describes CVE-2026-111497 as an “out-of-bounds write” that “permits remote code execution.” CISA added it to the KEV catalog on October 27. That catalog only lists flaws with evidence of exploitation. CISA’s entry warns that a remote, unauthenticated attacker could corrupt memory, leak data, crash the decoder, or potentially run code using “a crafted Brotli-compressed stream.” The agency gave U.S. federal agencies until November 10 to fix it.
One caveat. CISA’s entry covers the Brotli library in general. Neither Apple nor CISA says the bug was exploited on a Vision Pro specifically. Apple’s note simply credits no researcher and lists the fix. Still, Vision Pro received the patch 19 days after Google’s fix and 13 days after the CISA listing, one day before the federal deadline. That is good reason not to leave the update sitting in Settings.
Apple shipped the same day across its platforms. MacRumors reported watchOS 27.2.1 and visionOS 27.2.1 together, alongside iOS and macOS point releases. Mac developer Michael Tsai flagged the visionOS notes on X:
How to install it
On the headset, open Settings → General → Software Update and install visionOS 27.2.1 (build 24N124, per iClarified). Turn on automatic updates on the same screen. Version 27.2.1 includes the earlier 27.2 fixes, so a headset still on an older build can go straight to it. Our visionOS 27.2 feature rundown covers the Siri AI and FaceTime changes from the October release.
The bigger picture for XR security
Headsets and smart glasses now get the same kind of patch cycle as phones, and they have the same supply-chain exposure through shared libraries like Brotli. This fall we’ve covered Google’s Android XR security bulletin and a Ray-Ban Meta app-signing bypass. Buyers comparing platforms in our Apple Vision Pro guide or Galaxy XR vs Vision Pro comparison should count update speed and transparency as a real feature.
Sources
- Apple: About the security content of visionOS 27.2.1
- Apple: About visionOS 27 updates
- CISA: Known Exploited Vulnerabilities catalog (CVE-2026-111497)
- NIST NVD: CVE-2026-111497
- Google: Brotli v1.2.1 release
- MacRumors: Apple releases watchOS 27.2.1 and visionOS 27.2.1
- iClarified: Apple releases visionOS 27.2.1